

The Ultimate Guide to AI Security
A curated Kiwi edition of IndustrialDay news, analysis, interviews, reviews, job moves, and related resources for AI Security.
What to know about AI Security
AI Security is an evolving field that focuses on safeguarding artificial intelligence systems and applications from emerging threats and vulnerabilities. As AI technologies become increasingly integrated into various enterprise operations and critical infrastructures, securing these systems is vital to prevent data breaches, unauthorized access, and manipulation by malicious actors.
This tag encompasses the latest advancements, studies, and industry collaborations aimed at enhancing security postures through AI-powered defenses, unified risk management, and innovative tools designed specifically for AI environments. By exploring stories tagged with AI Security, readers gain insights into how organizations are leveraging AI to detect, respond to, and prevent sophisticated cyber threats, including those targeting cloud environments, hybrid infrastructures, and AI-driven applications.
Stay informed about global research, corporate initiatives, and technology partnerships that underscore the importance of AI-focused security practices. Whether you are a security professional, IT manager, or simply interested in the intersection of AI and cybersecurity, these updates offer valuable perspectives on protecting AI systems against evolving risks in today's digital landscape.
Kiwi AI Security News
Regional stories with direct local relevance
Trade Me dominates NZ cyber awards with triple win
Trade Me's security work has been recognised for helping keep its platform safer, as judges honoured its team, leader and AI project.

SiteHost launches local AI platform for New Zealand
Businesses wary of offshore AI will be able to keep requests in New Zealand, with usage-based billing and no upfront fee.
New Zealand online scams surge as trust is exploited
Online shoppers in New Zealand face a sharper risk of fraud as fake stores and remote access attacks exploit trusted digital services.

Safety isn't just a launch state, it's a discipline
AI wellbeing coaches face persistent probing, and the company says health tools must be monitored daily as attacks grow more sophisticated.
From cryptographic debt to boardroom accountability: A CEO's blueprint for post-quantum resilience
Quantum theft could expose sensitive records years from now, turning today's encrypted files into a board-level liability for Kiwi firms.

From biometrics to zero trust secures physical-digital divide
Organisations are pairing biometrics with layered access controls as cyber and physical threats converge inside data centres and other sensitive facilities.
Analyst Insights
Research and market analysis connected to AI Security
Ping Identity named leader in Gartner's new CIAM report
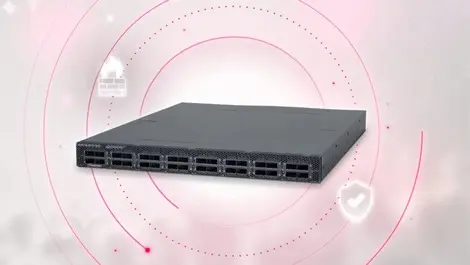
Check Point launches AI-scale security orchestrator 200
Check Point launches firewall subscription for AI security
Reco raises USD $55 million as AI agent security grows
RSA launches Agent ID for regulated AI agent control
Featured News
VAST Data targets AI data sovereignty with DataEnclave
Enterprises and governments could run AI on sensitive data without exposing it, as the technology targets sovereignty rules across APAC.
Interview: Cloudera says open-ended AI spending is over
Enterprises are now demanding proof of value and tighter controls as AI budgets face scrutiny over compute costs and deployment choices.
Zscaler takes zero trust beyond the corporate network
Critical infrastructure operators are using cellular links to secure distributed assets as outages and spoofing raise the stakes for resilience.
Workiva: The secret compliance and reporting arms race
Driven by improved tooling, finance teams are meeting higher standards as regulators and analysts scrutinise disclosures faster.
Governance controls are crucial for AI adoption and modernisation
Trusted partners and tighter guardrails are becoming essential as AI agents expand the attack surface and put data sovereignty on the line.
Mimecast CEO: Agentic AI threat novel but not entirely new
Hidden AI risks are already widespread in workplaces, with Mimecast saying users are driving shadow tools and most exposure still starts with people.
Jamf launches AI Governance to enhance visibility, security
IT teams can now track AI models on Apple fleets to curb data leaks and token spend as businesses wrestle with shadow AI.
AI models expose new attack surfaces through misconfiguration
Misconfigured models are giving attackers a fresh route into cloud systems, raising the risk of data theft and service compromise.

AI adoption races ahead of governance in businesses
Only one in six staff are getting enough AI training, leaving firms exposed to poor decisions, shadow tools and weak returns.
Expert Columns
Seven Cyber Controls Businesses Can No Longer Afford to Overlook
In the AI era, channel value is being redefined
Stop saying AI hacked the system
Why trusted 'Customer Context' is critical in the agentic AI era
AI closes vulnerability window as zero-day exploits surge
Unlocking potential: How expanding leadership pathways for women strengthens cybersecurity
The future of autonomous security
AI visibility becoming the new boardroom blind spot
AI is testing the limits of Zero Trust

Why AI infrastructure planning must happen now
Interviews
Interviews and video coverage from the networkRecent AI Security News
Fortinet brings AI security to Equinix distributed hub
Enterprises can now inspect AI prompts and responses across clouds and data centres through a validated Fortinet-Equinix architecture.
AI attacker blocked by microsegmentation in Anthropic test
The result underscores how microsegmentation can stop an AI intruder from turning one compromised machine into wider network access.
Illumio warns AI authority is outpacing security controls
Most firms now hand AI decisions once reserved for staff, but fewer than half can fully audit its actions, a new survey found.
CrowdStrike launches tools to detect risky AI agents
The tools are designed to spot rogue AI behaviour and simulate attacks before autonomous systems can reach critical data or systems.
JFrog adds AI security controls for developer tools
Security teams can now spot unauthorised AI tools on developer machines before they reach production, as JFrog extends its controls.
Thoughtworks urges tighter controls as AI agents spread
Companies are being pushed to secure, monitor and budget for AI systems as agents take on longer tasks and strain review processes.
CrowdStrike to buy Fiddler AI & Dreadnode in AI push
The moves underline how security vendors are racing to control AI agents as businesses widen their use of automated software across operations.
Tanium joins OpenAI cyber programme for threat research
The limited access will help its hunters and engineers turn OpenAI models into detections, vulnerability work and stronger platform defences.
CrowdStrike & Dell launch AI Factory security package
The package aims to help enterprises secure AI systems from infrastructure to agents as they rush to deploy production workloads.
Palo Alto Networks launches unified SaaS cloud security
Security teams may gain a clearer picture of connected threats as Palo Alto Networks folds SaaS, cloud, identity and AI risks into one platform.
Sweet launches virtual patching for cloud & AI workloads
Security teams can now block exploit attempts on live cloud and AI workloads while permanent fixes wait to clear testing and release processes.
CISOs lag on AI governance as board oversight trails
Many large firms still lack clear AI oversight, with just 7% of CISOs at companies above USD $10 billion in revenue owning the governance brief.
Microsoft adds security tools for AI agents in 365
Security teams will soon be able to limit and monitor AI agents in Microsoft 365 as the company treats them as potential insider risks.
Oracle launches AI security mesh with OpenAI to fix flaws
The service aims to help enterprises spot and repair vulnerabilities faster across cloud and on-premises systems, while keeping human approval in place.
Alice helps train NVIDIA Nemotron models for safety
The collaborations aim to curb harmful behaviour in open AI models while preserving performance, as enterprises face growing prompt-injection risks.
Oracle unveils Deep Trust AI Architecture for enterprises
The framework is meant to help companies control security, privacy and business rules as AI agents and generated software spread through enterprise systems.
Growing firms hit hardest by unauthorised data access
Companies with 500 to 999 staff were most likely to report unauthorised data access, with 40% saying they had been hit in the past year.
HITRUST adds AI security tools & third-party risk updates
Businesses facing surging AI and supplier reviews now have new HITRUST tools to cut questionnaire burden and tighten certification checks.
Mid-sized firms hit hardest by unauthorised data access
Mid-sized businesses are facing the sharpest exposure, with four in 10 reporting sensitive data access by unauthorised identities in the past year.
Endor Labs adds BYOK support for AI security scans
The new option should ease approval hurdles for regulated firms that need AI code scans without handing source code to vendor-selected models.